

Threat Wire: GitHub CLI Token Leaks via AI Gateways
Critical OAuth token leakage in LiteLLM logs impacts GitHub CLI security. Exploitation allows unauthorized repository access and supply chain poisoning.
Critical OAuth token leakage in LiteLLM logs impacts GitHub CLI security. Exploitation allows unauthorized repository access and supply chain poisoning.

CVSS 9.8 RCE in Citrix NetScaler ADC and Gateway under active exploitation. Attackers deploying web shells and FreeBSD malware. Immediate patching required.
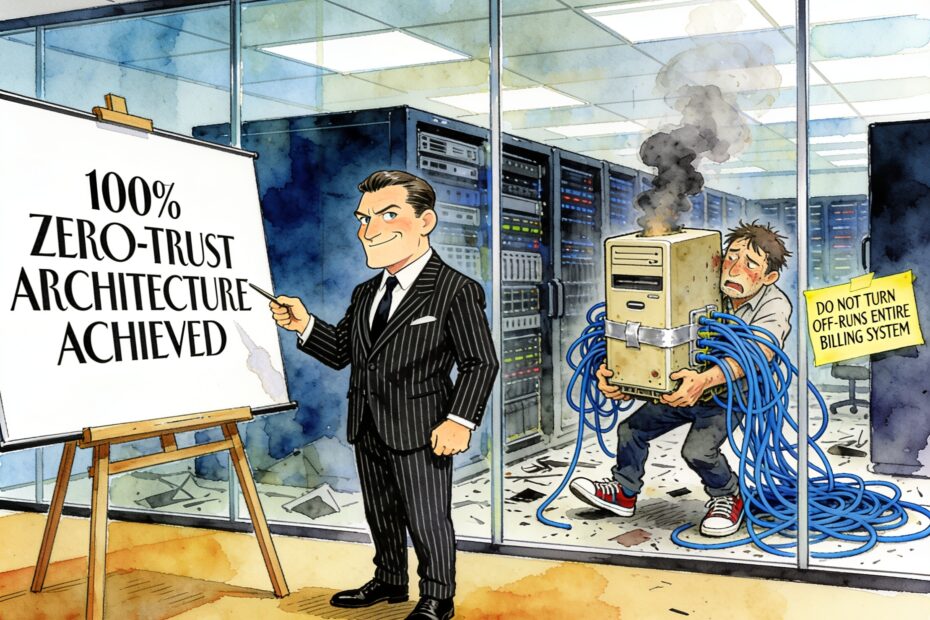
“We have officially achieved 100% Zero-Trust compliance across the enterprise, gentlemen, by ensuring nobody trusts anything IT tells them.”
CVSS 9.8 authentication bypass in Ivanti Connect Secure enables remote code execution. CISA KEV confirms active exploitation against enterprise perimeters.
 Helpdesk.ca Assistant
Please enter your details to start chatting.